Limitations of standard TCP
Most applications such as email, HTTP, FTP and TCP-based SSL VPN use TCP. Standard TCP congestion control estimates the safe transmission rate in the network and has throughput fall-back mechanisms in case of suspected congestion. TCP performance can be limited by the host TCP stack implementation, processing speeds of routers, bandwidth available in intermediate links, packet loss, round-trip delay, changes in round-trip delay and other factors.
Standard TCP also has two major drawbacks in long-delay environments:
- Long delays in the network lead to suboptimal window size calculations.
- The TCP slow start mechanism avoids bursts on low-latency links and doubles throughput every round trip, which leads to slow TCP throughput over long-delay links.
How the TCP Accelerator works
The TCP Accelerator is a fully transparent performance-enhancing proxy that optimizes TCP sessions on the fly. It uses these mechanisms to improve TCP performance:
- HighSpeed TCP: optimizes TCP performance for high-speed, high-delay networks.
- Window scaling: the TCP Window Scale option sets the optimal window sizes, to avoid the throughput limit of a suboptimal TCP window size.
- Selective acknowledgement: when packets are lost and cannot be recovered by packet loss recovery, the sender is notified to retransmit only the missing packets.
- Local congestion and flow control: the TCP Accelerator splits an end-to-end TCP connection transparently and operates each link separately, with HighSpeed TCP congestion and flow control metrics for each.
- Local acknowledgements: acknowledgements are sent locally between the proxy and server, and between the proxy and client, to avoid idle time waiting for acknowledgements.
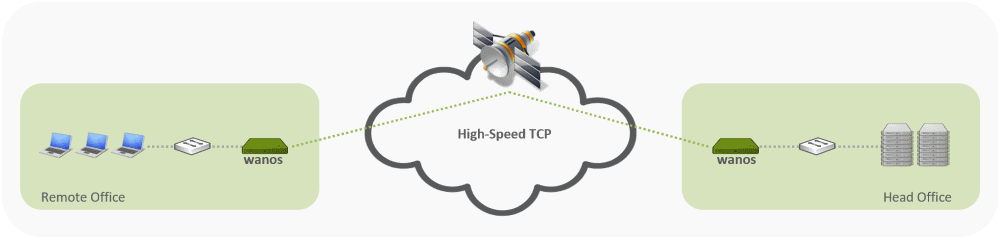
Where TCP acceleration is used
- Application performance and user experience over VPN, SD-WAN and long-delay networks.
- Backup, replication and storage traffic over MPLS WAN links.
- As a standalone TCP performance-enhancing proxy (TCP-PEP), for example at satellite hub sites or wireless ISPs (WISP).
- For enterprises, at both remote and central sites.
Results
The result of these features working together is faster file transfers for TCP-based applications. Where TCP throughput is suboptimal due to the limitations of standard TCP or network conditions, speed improvements of 2–10x are expected. The improvement depends on the severity of the conditions that hinder performance, and on the optimization ratio of the other acceleration features: stream compression, deduplication and packet loss recovery.
Deployment and policies
From v4.2.9 the TCP Accelerator runs in full transparency mode in bridge deployments, so no routing configuration is needed. When TCP-X is enabled, TCP sessions are optimized by default; TCP-X policies include or exclude the TCP traffic to optimize, by source, destination and optional TCP port.
Asymmetric routing (where packets take a different path back) hides half of a session from Wanos. TCP-X asymmetric route detection handles server-side, client-side and full asymmetry.
Some conditions exist where the TCP Accelerator will not enhance performance: non-TCP protocols such as UDP-based video or audio streaming, and optimal network conditions such as high-speed, low-latency environments.